AI Security
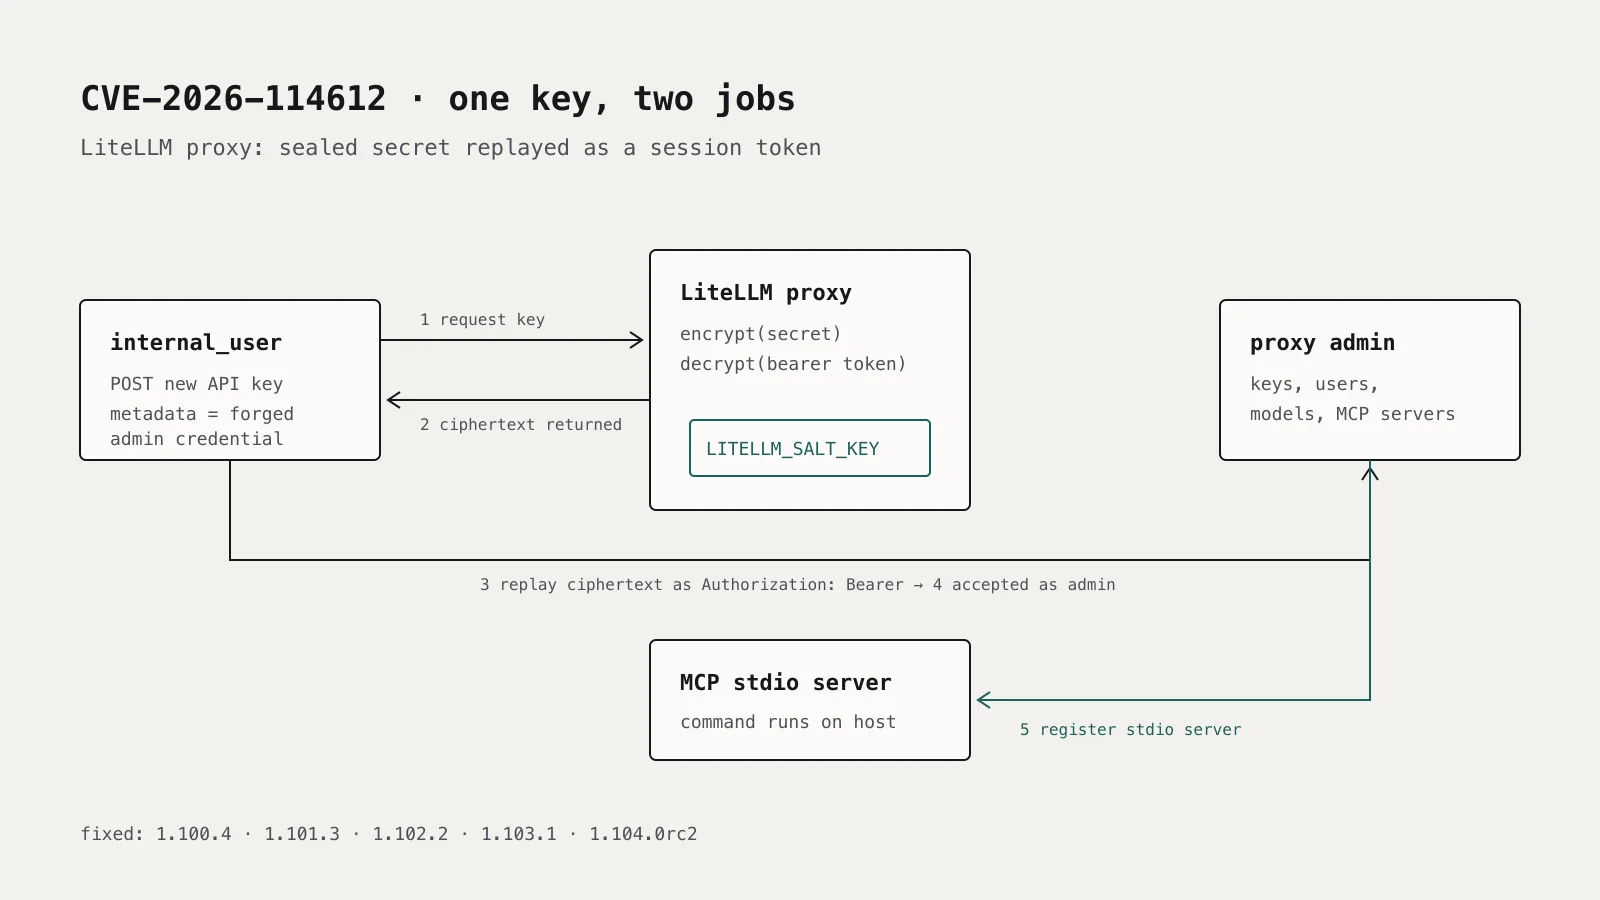
LiteLLM CVE-2026-114612: how one shared key turned an internal user into proxy admin
LiteLLM used one encryption key both to seal stored secrets and to mint login tokens, so an internal user could get the proxy to encrypt a forged admin credential for them. Here is who is exposed, which releases fix it, and the follow-up checks worth doing.
6 min read